This record tracks a ransomware attack claimed by the
aurora group against
Evosys Laser GmbH. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
98days open
t1 · Published
t2 · Pending
Business Category
Manufacturing / Engineering
Indexed by Breach House
July 30, 2026
Disclosed / Notified
Not disclosed yet
Attack Summary
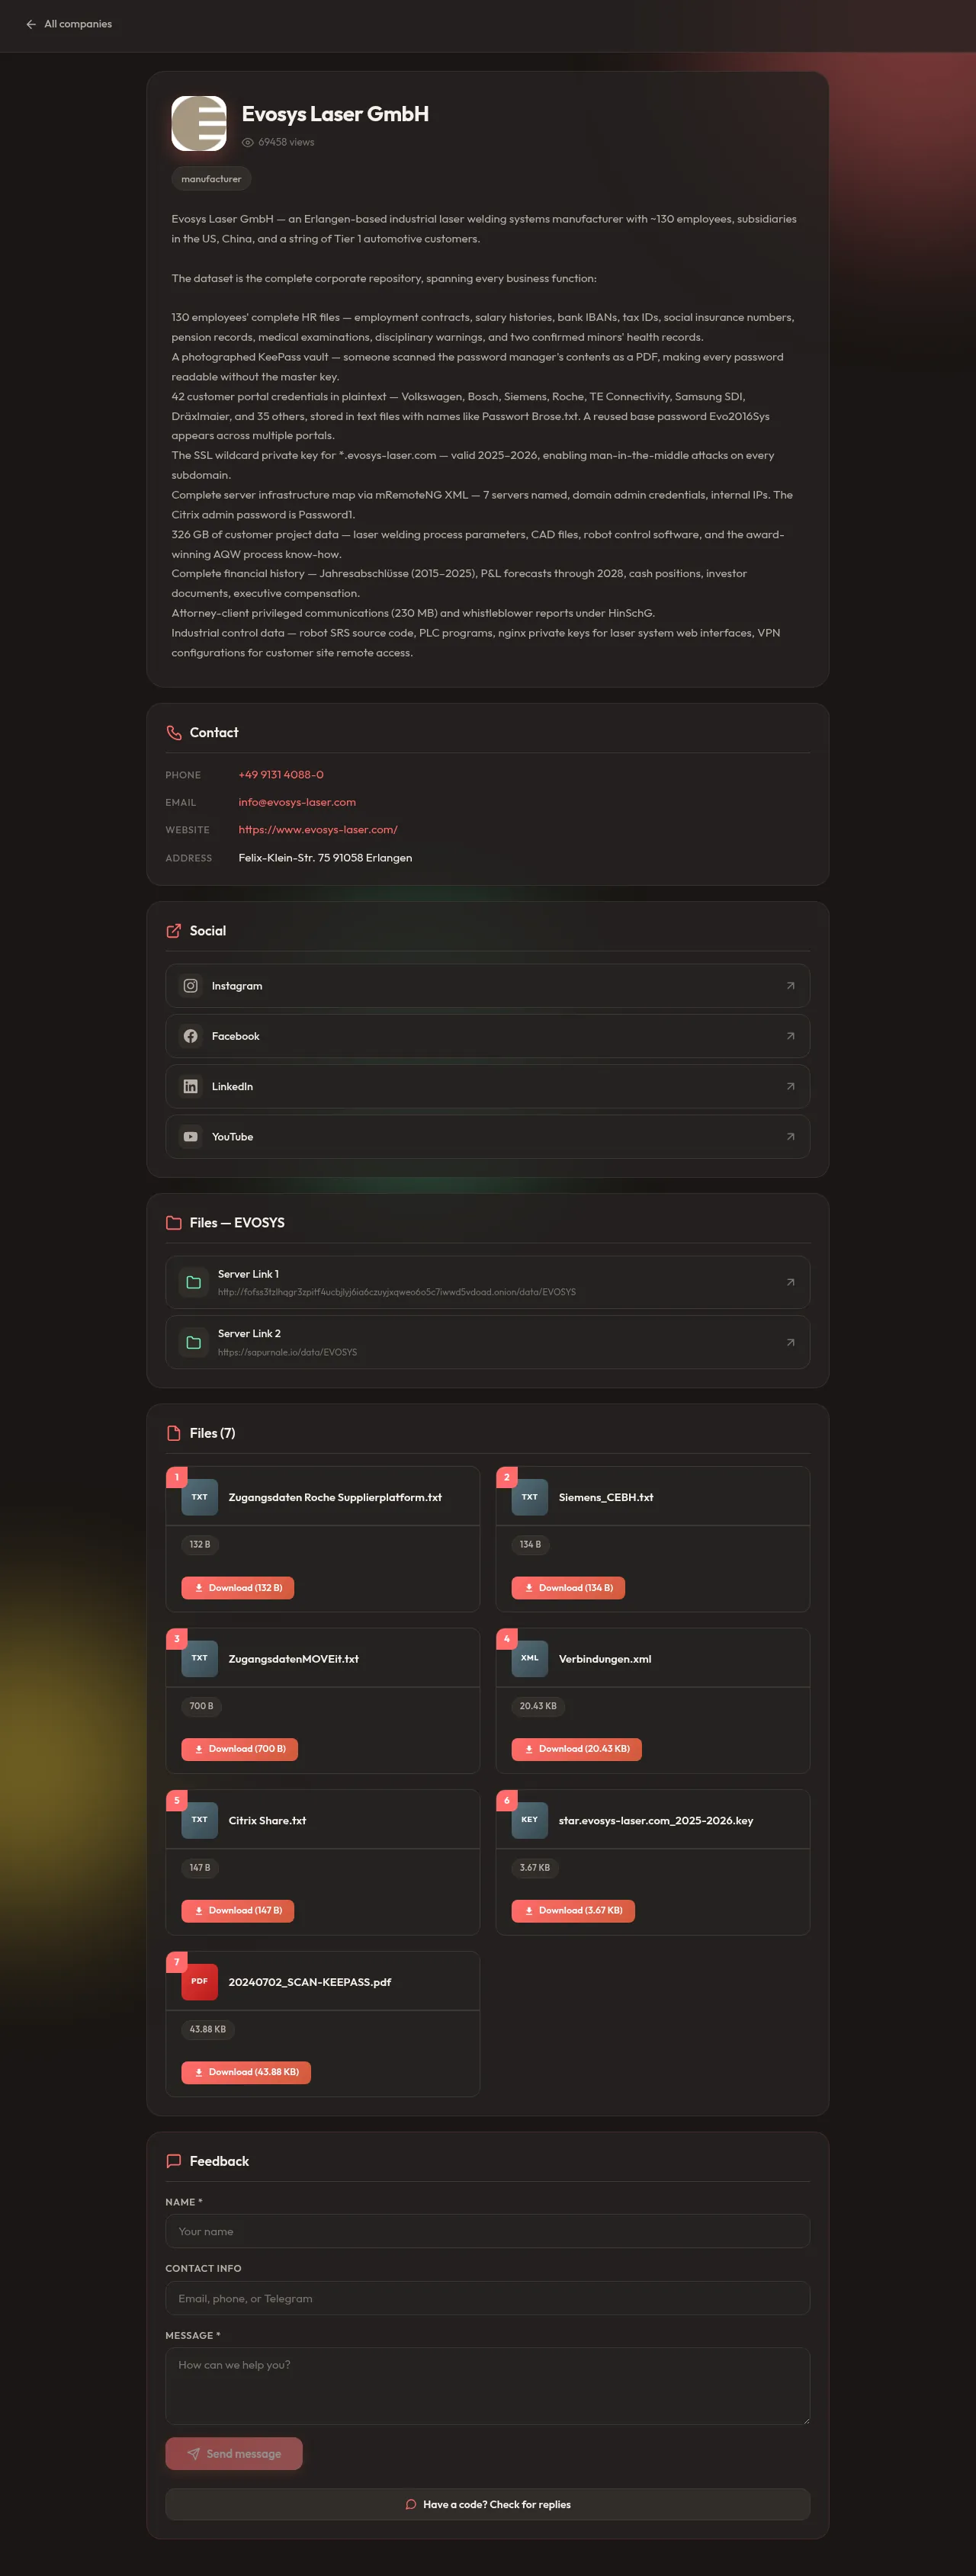
[manufacturer] Evosys Laser GmbH — an Erlangen-based industrial laser welding systems manufacturer with ~130 employees, subsidiaries in the US, China, and a string of Tier 1 automotive customers.
The dataset is the complete corporate repository, spanning every business function:
130 employees' complete HR files — employment contracts, salary histories, bank IBANs, tax IDs, social insurance numbers, pension records, medical examinations, disciplinary warnings, and two confirmed minors' health records.
<censored>
<censored>
Complete server infrastructure map via mRemoteNG XML — 7 servers named, domain admin credentials, internal IPs. The Citrix admin password is Password1.
326 GB of customer project data — laser welding process parameters, CAD files, robot control software, and the award-winning AQW process know-how.
Complete financial history — Jahresabschlüsse (2015–2025), P&L forecasts through 2028, cash positions, investor documents, executive compensation.
Attorney-client privileged communications (230 MB) and whistleblower reports under HinSchG.
Industrial control data — robot SRS source code, PLC programs, nginx private keys for laser system web interfaces, VPN configurations for customer site remote access.
Leak Screenshots
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-10-02. Verdict evidence: [A1] Own Files section provides published server links
Capture history —
4 day(s) tracked. Content is locked.
Showing the latest capture only
Unlock the 4 captures already taken.
What's In This Leak
Composition analysis from Have I Been Ransom · ransomware leak.
—
Identity documents present
json
56,904
records · 87 files
xlsx
16,763
records · 167 files
••••
••••••••
records · ••••• files
••••
••••••••
records · ••••• files
••••
••••••••
records · ••••• files
••••
••••••••
records · ••••• files
••••
••••••••
records · ••••• files
Identity documents
••••
••% of records
Full composition is locked
Unlock the remaining 9 file type(s), the corporate vs personal email split.
Dark Web Exposure
Cross-referenced against HaveIBeenRansom's dark-web index of ransomware leaks, breaches & infostealer logs.
0
found in Infostealer logs
0
found in Traditional breaches
0
found in Ransomware leaks
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
Full exposure is locked
See every breached email, the internal-vs-external split and each leak source behind this victim.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.