This record tracks a ransomware attack claimed by the
aurora group against
FREYWILLE. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
72days open
t1 · Published
t2 · Pending
Business Category
Retail / E-commerce
Indexed by Breach House
August 11, 2026
Disclosed / Notified
Not disclosed yet
Attack Summary
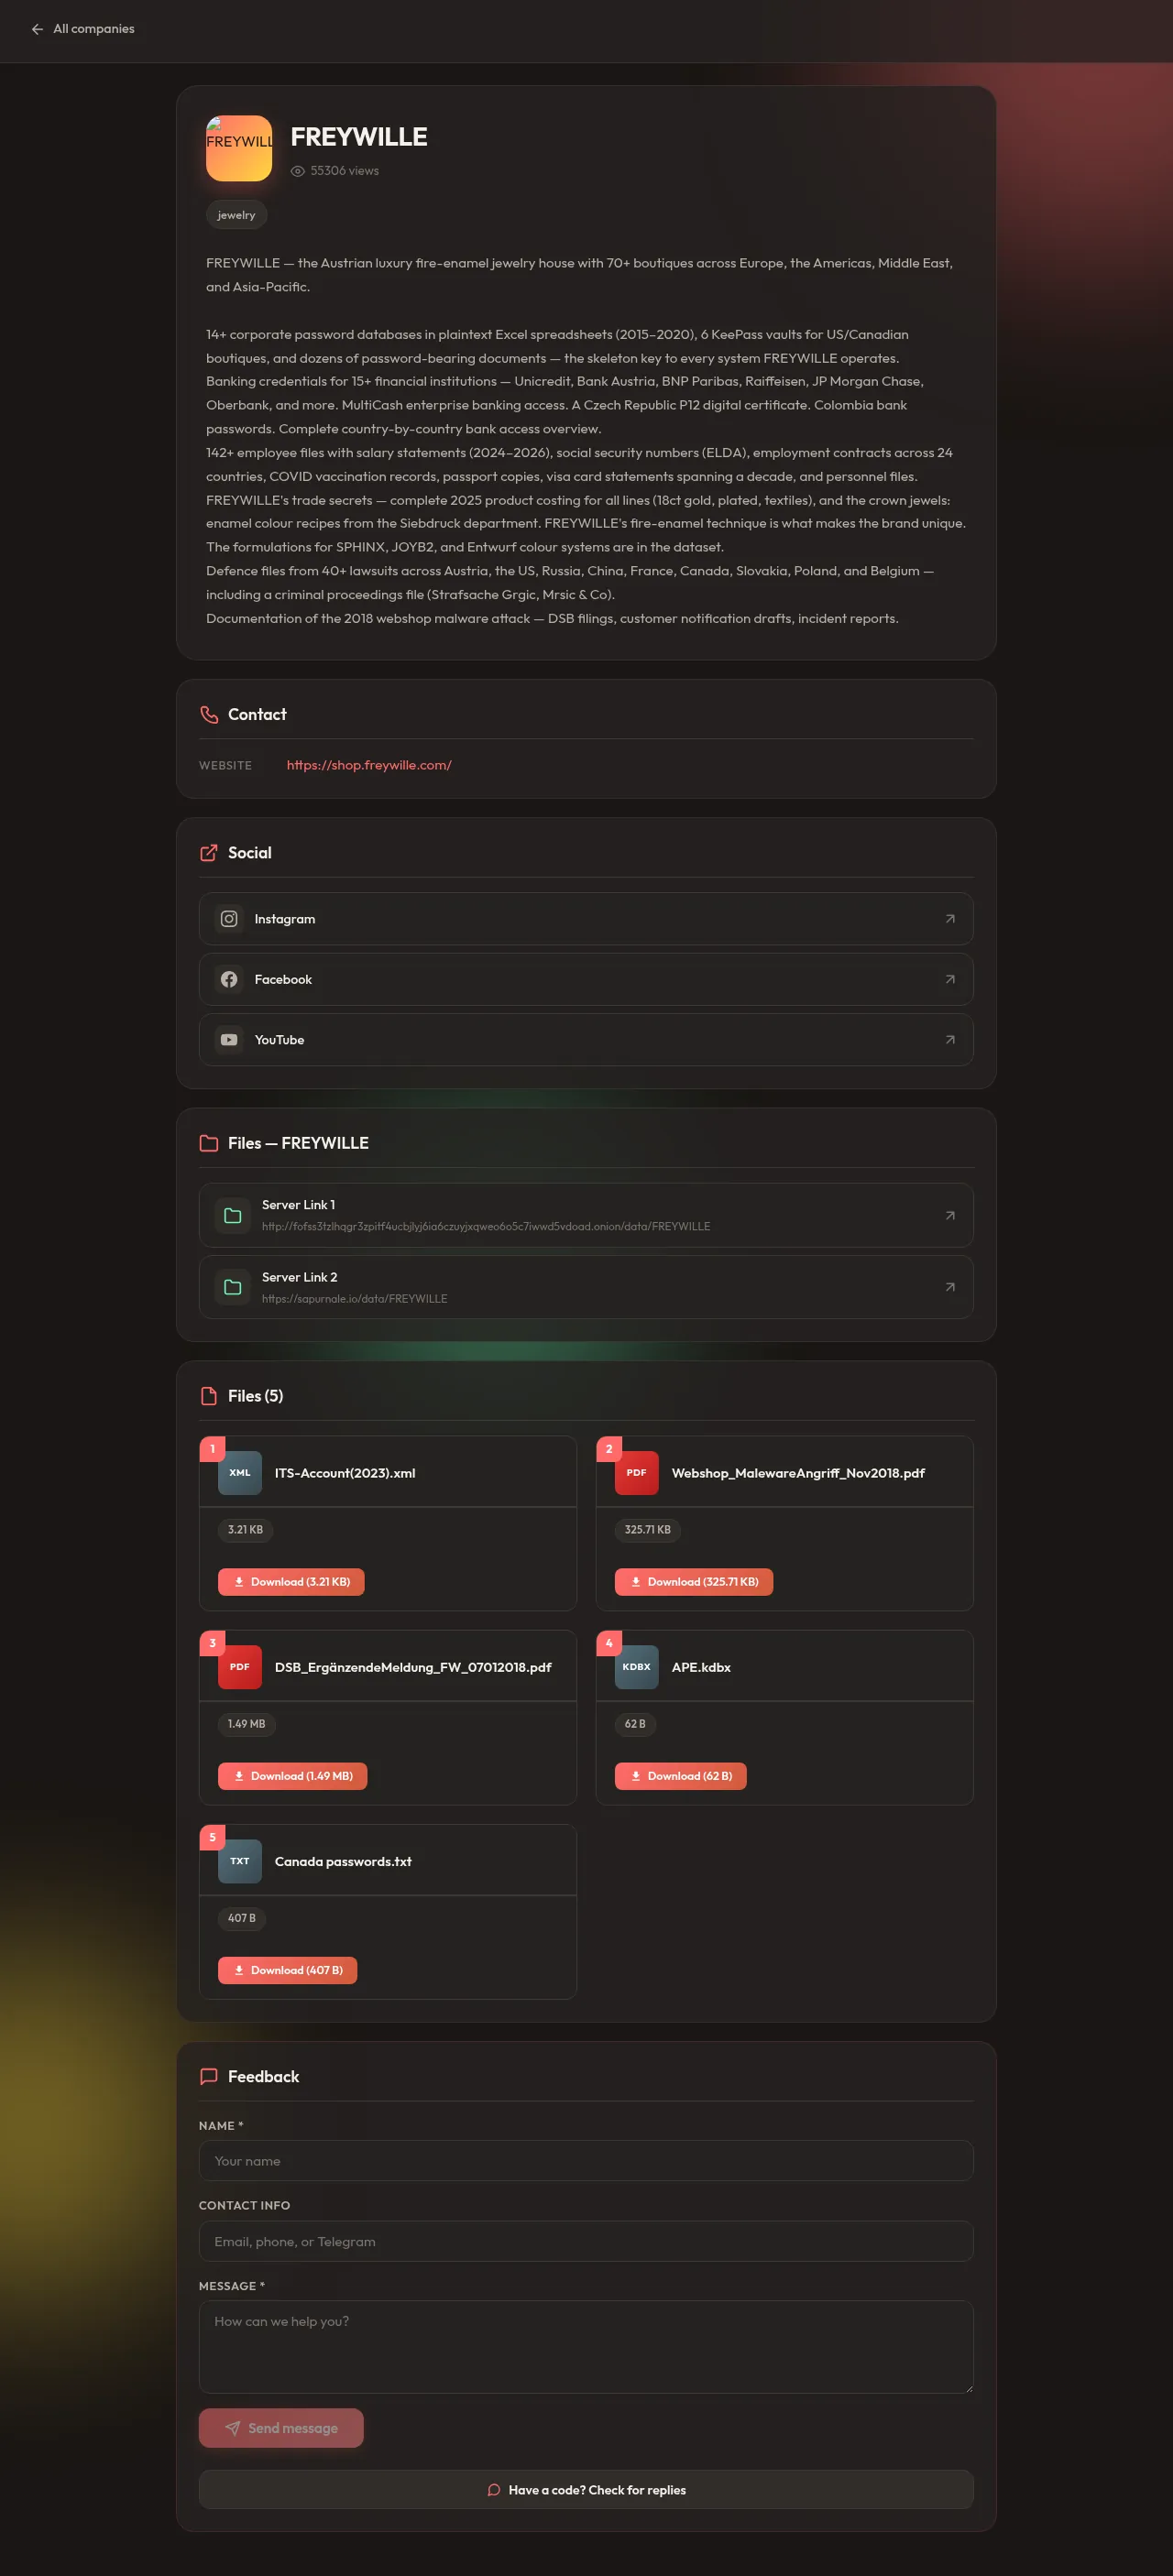
[jewelry] FREYWILLE — the Austrian luxury fire-enamel jewelry house with 70+ boutiques across Europe, the Americas, Middle East, Russia/CIS, and Asia-Pacific.
<censored>
<censored>
142+ employee files with salary statements (2024–2026), social security numbers (ELDA), employment contracts across 24 countries, COVID vaccination records, passport copies, visa card statements spanning a decade, and personnel files.
FREYWILLE's trade secrets — complete 2025 product costing for all lines (18ct gold, plated, textiles), and the crown jewels: enamel colour recipes from the Siebdruck department. FREYWILLE's fire-enamel technique is what makes the brand unique. The formulations for SPHINX, JOYB2, and Entwurf colour systems are in the dataset.
Defence files from 40+ lawsuits across Austria, the US, China, France, Canada, Slovakia, Poland, and Belgium — including a criminal proceedings file (Strafsache Grgic, Mrsic & Co).
Documentation of the 2018 webshop malware attack — DSB filings, customer notification drafts, incident reports.
Leak Screenshots
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-10-02. Verdict evidence: [A1] Own Files section provides published server links
Capture history —
4 day(s) tracked. Content is locked.
Showing the latest capture only
Unlock the 4 captures already taken.
What's In This Leak
Composition analysis from Have I Been Ransom · ransomware leak.
—
Identity documents present
csv
151,080
records · 175 files
xls
149,720
records · 149 files
••••
••••••••
records · ••••• files
••••
••••••••
records · ••••• files
Identity documents
••••
••% of records
Full composition is locked
Unlock the remaining 2 file type(s), the corporate vs personal email split.
Dark Web Exposure
Cross-referenced against HaveIBeenRansom's dark-web index of ransomware leaks, breaches & infostealer logs.
0
found in Infostealer logs
0
found in Traditional breaches
0
found in Ransomware leaks
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
Full exposure is locked
See every breached email, the internal-vs-external split and each leak source behind this victim.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.