IHG Hotels & Resorts (Estate)
BYODThis record tracks a ransomware attack claimed by the BYOD group against IHG Hotels & Resorts (Estate). It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
IHG Hotels & Resorts Estate is a prominent hospitality, food and beverage, and tourism enterprise operating globally with significant physical properties and digital services across the United States and international markets. The entity provides lodging, dining, travel services, and resort experiences to guests seeking accommodation and on-site amenities within the broader hospitality sector. In the context of this threat-intelligence index, IHG Hotels & Resorts Estate is documented as a ransomware victim associated with the BYOD threat actor category. This classification reflects the security posture and exposure profile of an organization whose operational technology and guest-facing systems may be targeted through bring-your-own-device practices. The listing serves as a neutral reference point for analysts tracking cyber incidents within the US hospitality and tourism landscape.
Leak Screenshots
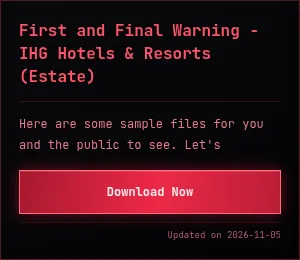
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-11-05. Verdict evidence: [H2] Download Mirror #1 - Password: BYOD
Capture history — 2 day(s) tracked. Content is locked.