Goodrich Logistics
DoommageddonThis record tracks a ransomware attack claimed by the Doommageddon group against Goodrich Logistics. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Goodrich Logistics operates in the United States as a full‑service transportation and logistics company, offering freight forwarding, warehousing, distribution, and supply‑chain management services to a diverse range of commercial clients. The firm’s infrastructure supports domestic and international shipping, leveraging a network of carriers and technology platforms to optimize cargo movement and inventory handling. As part of the broader transportation, travel, and logistics sector, Goodrich Logistics plays a critical role in ensuring timely delivery of goods across multiple industries. The company has been identified in a threat‑intelligence index as a ransomware victim associated with the Doommageddon threat actor, reflecting the growing cyber‑risk exposure within logistics operations.
Leak Screenshots
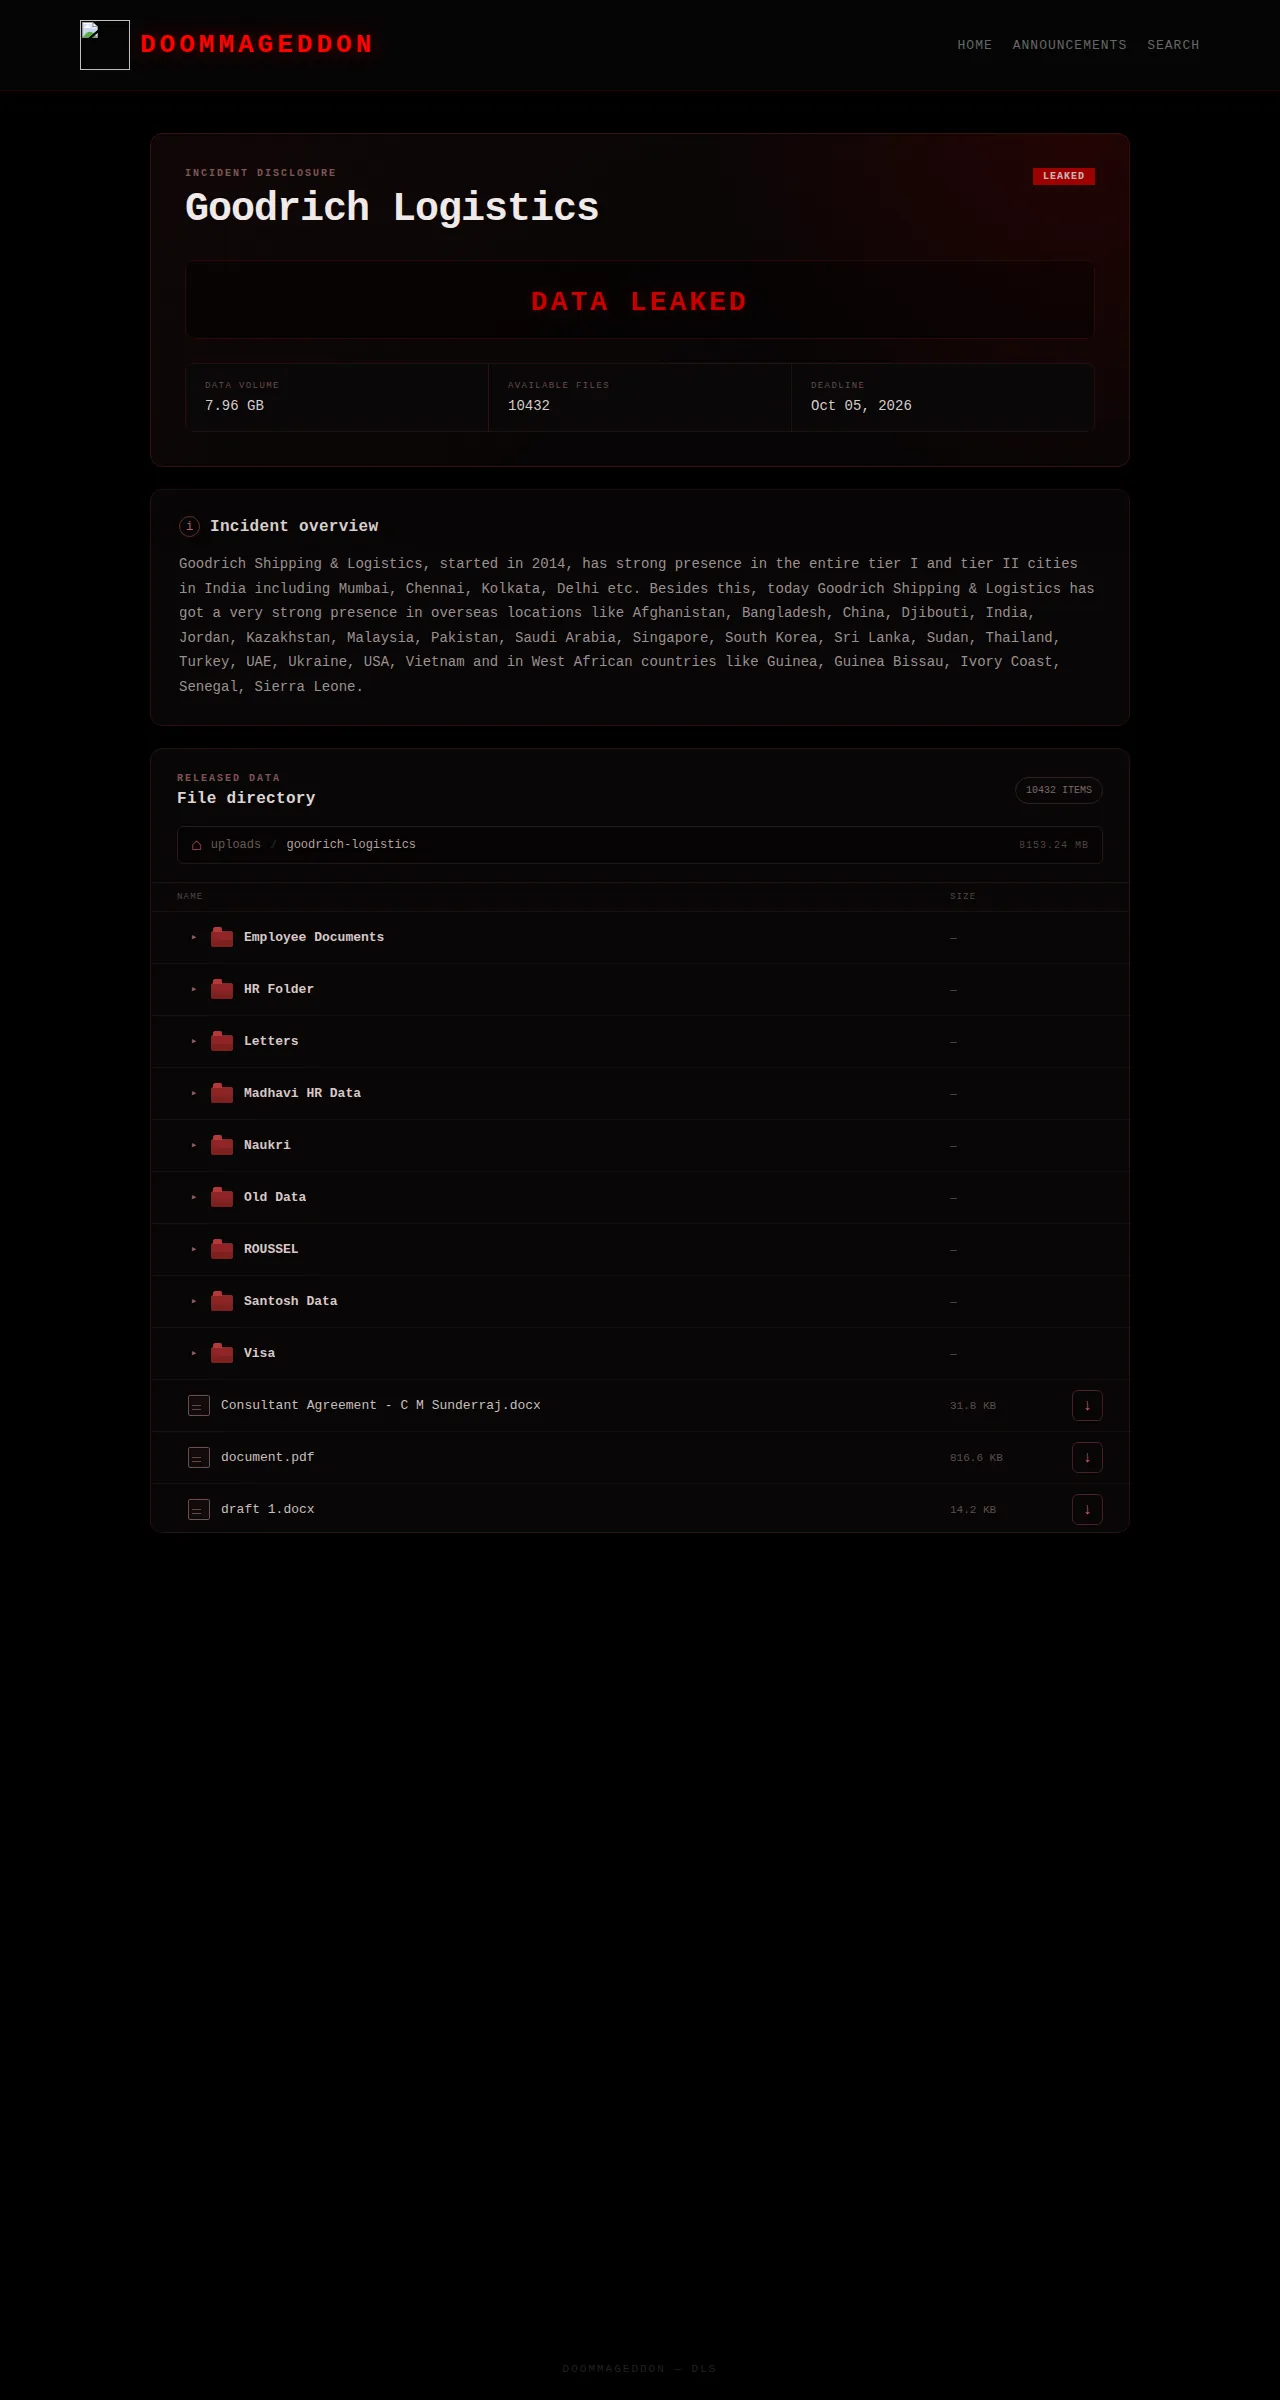
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-08. Verdict evidence: [H4] 12 files: consultant agreement - c m sunderraj.docx, document.pdf, draft 1.docx, goodrich logistics private limited amc.pdf, komal_nikam_cv.pdf, lakshmi ca.pdf
Capture history — 9 day(s) tracked. Content is locked.