WARNING
EndZoneThis record tracks a ransomware attack claimed by the EndZone group against WARNING. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
WARNING is a ransomware victim entity operating within the cybersecurity sector, associated with the threat actor EndZone. As a ransomware victim, WARNING represents an organization or entity impacted by malicious software activity targeting data integrity and operational continuity. The entity's specific sector and geographic location are not detailed in provided data; its primary association here is its classification as a ransomware victim linked to EndZone within the threat-intelligence index. This listing serves to catalog the entity's relationship with the identified threat actor for analytical and defensive reference purposes. The description remains neutral and avoids speculation regarding incident specifics, data exposure, or resolution details.
Leak Screenshots
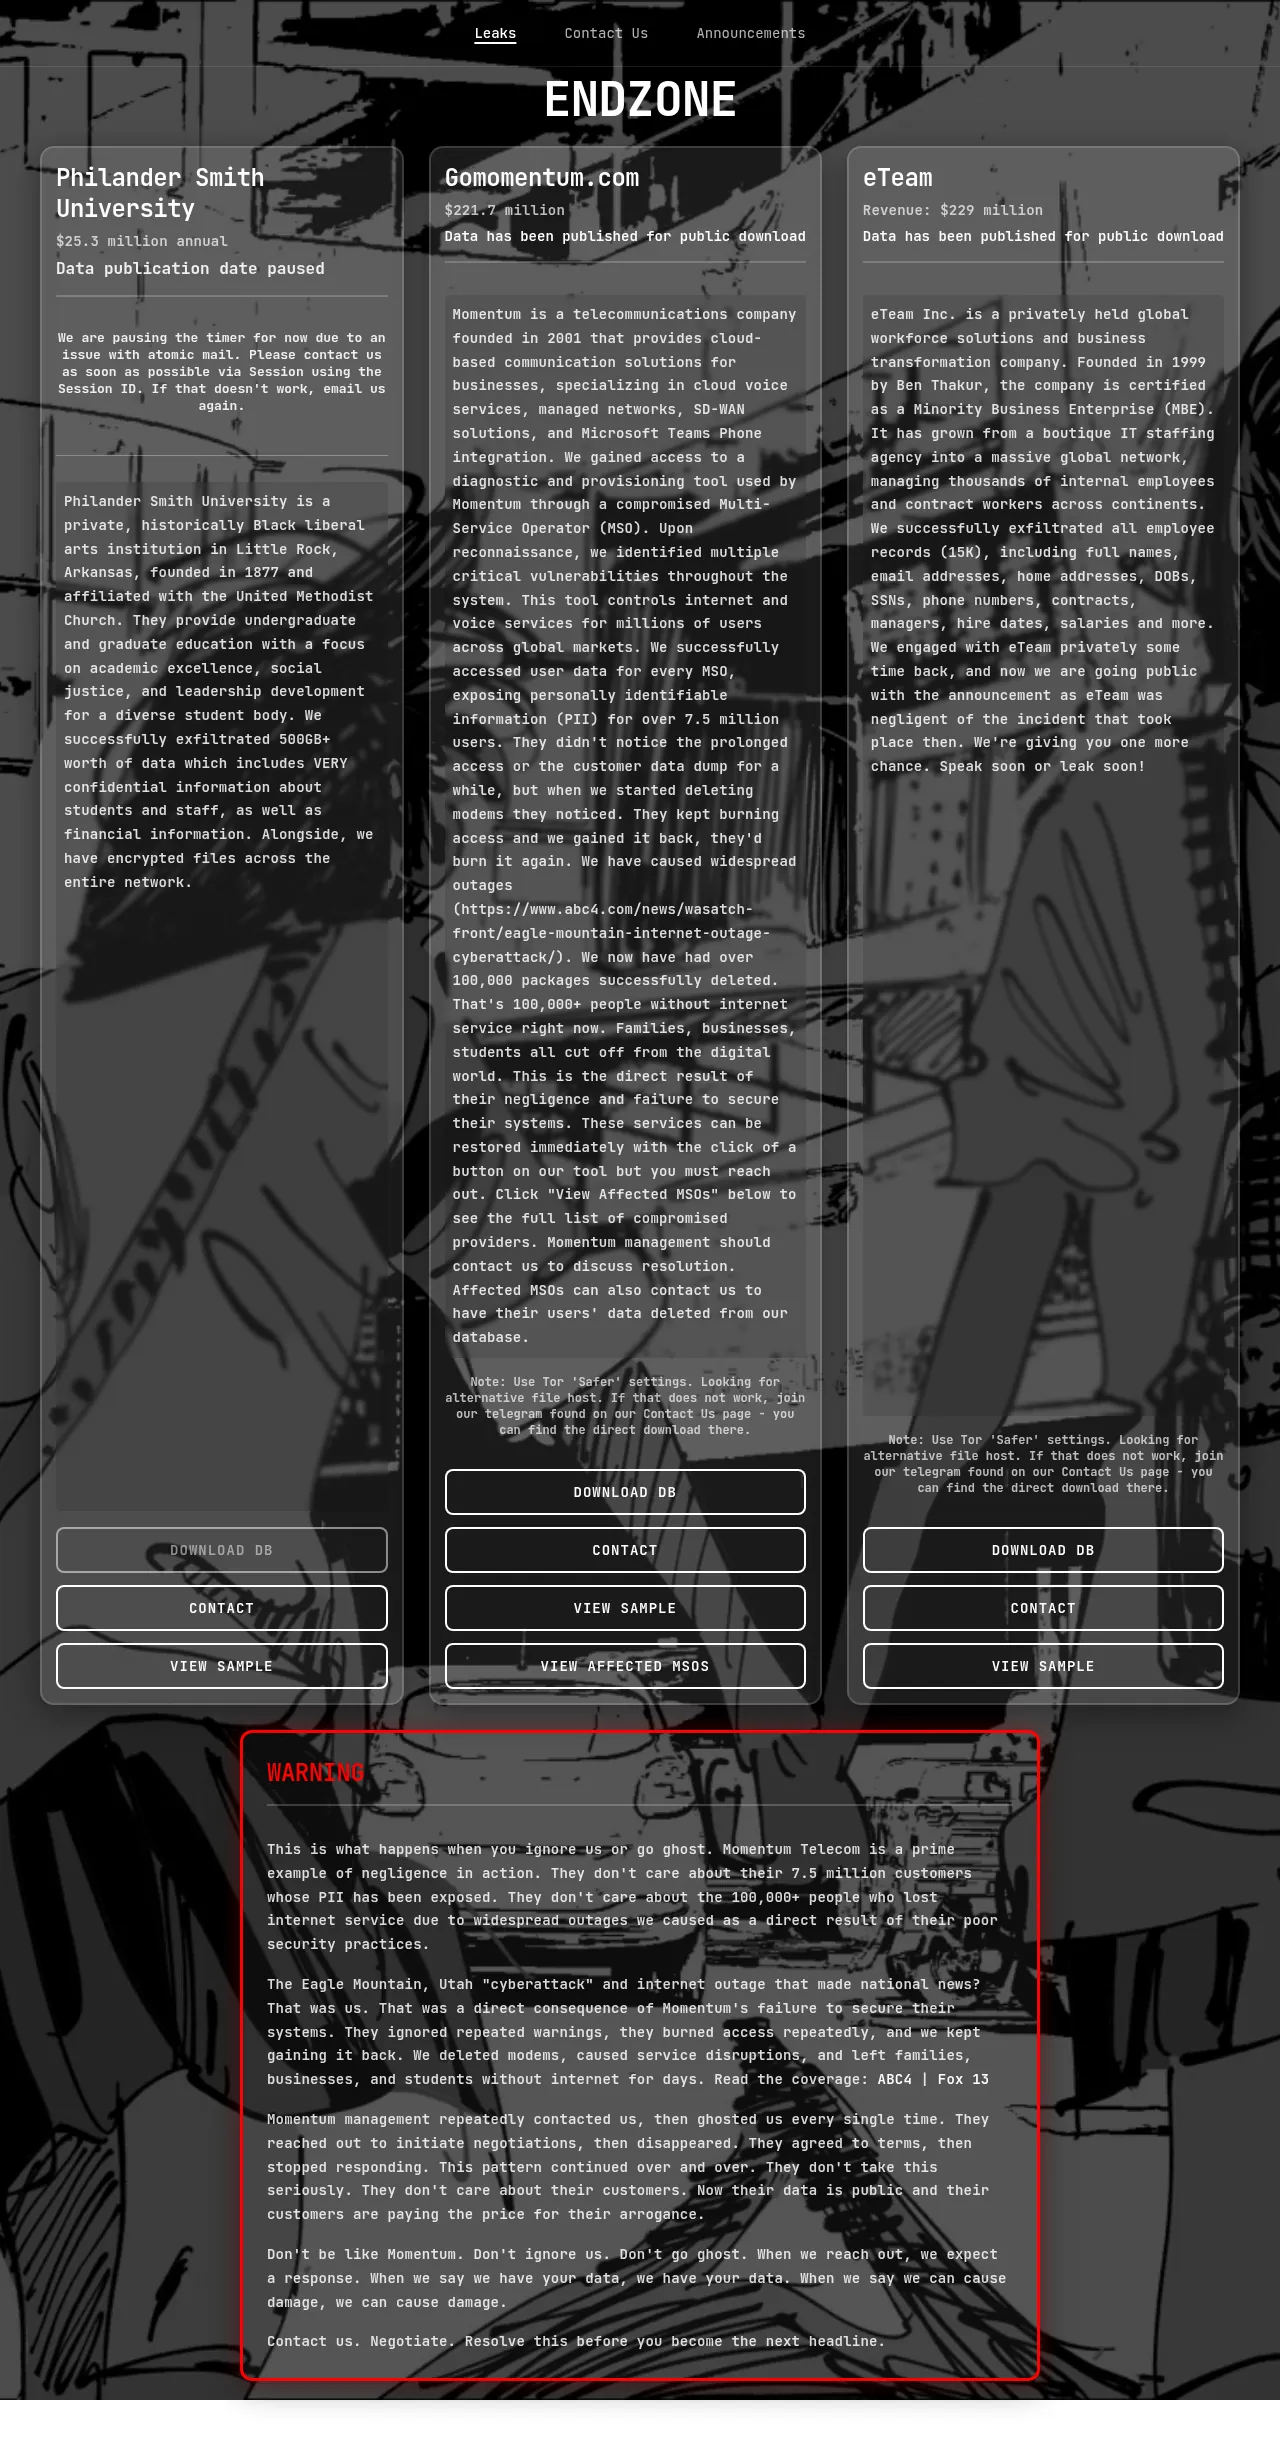
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-19. Verdict evidence: [H10] Momentum management repeatedly contacted us, then ghosted us every single time. They reached out to initiate negotiations, then disappeared. They agreed to terms, then stopped responding. This p
Capture history — 4 day(s) tracked. Content is locked.