Italy
ImNotAVillainThis record tracks a ransomware attack claimed by the ImNotAVillain group against Italy. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Italy is a nation-state operating within the information technology sector, providing digital infrastructure, services, and enterprise solutions across multiple industries. As a ransomware victim listing type in this threat-intelligence index, Italy is documented in relation to the ImNotAVillain threat actor. This entry captures the geographic and sectoral context of the affected entity without disclosing specific incident details such as data stolen, records impacted, ransom demands, or breach confirmation. The catalog description maintains a neutral, authoritative tone suitable for cybersecurity professionals monitoring ransomware activity and threat actor attribution. Italy's inclusion reflects its role within the IT landscape as a subject of ransomware-related threat intelligence indexing.
Leak Screenshots
8 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-19. Verdict evidence: [M1] Personal information on more than 130K federal officers across top departments has been obtained by us.
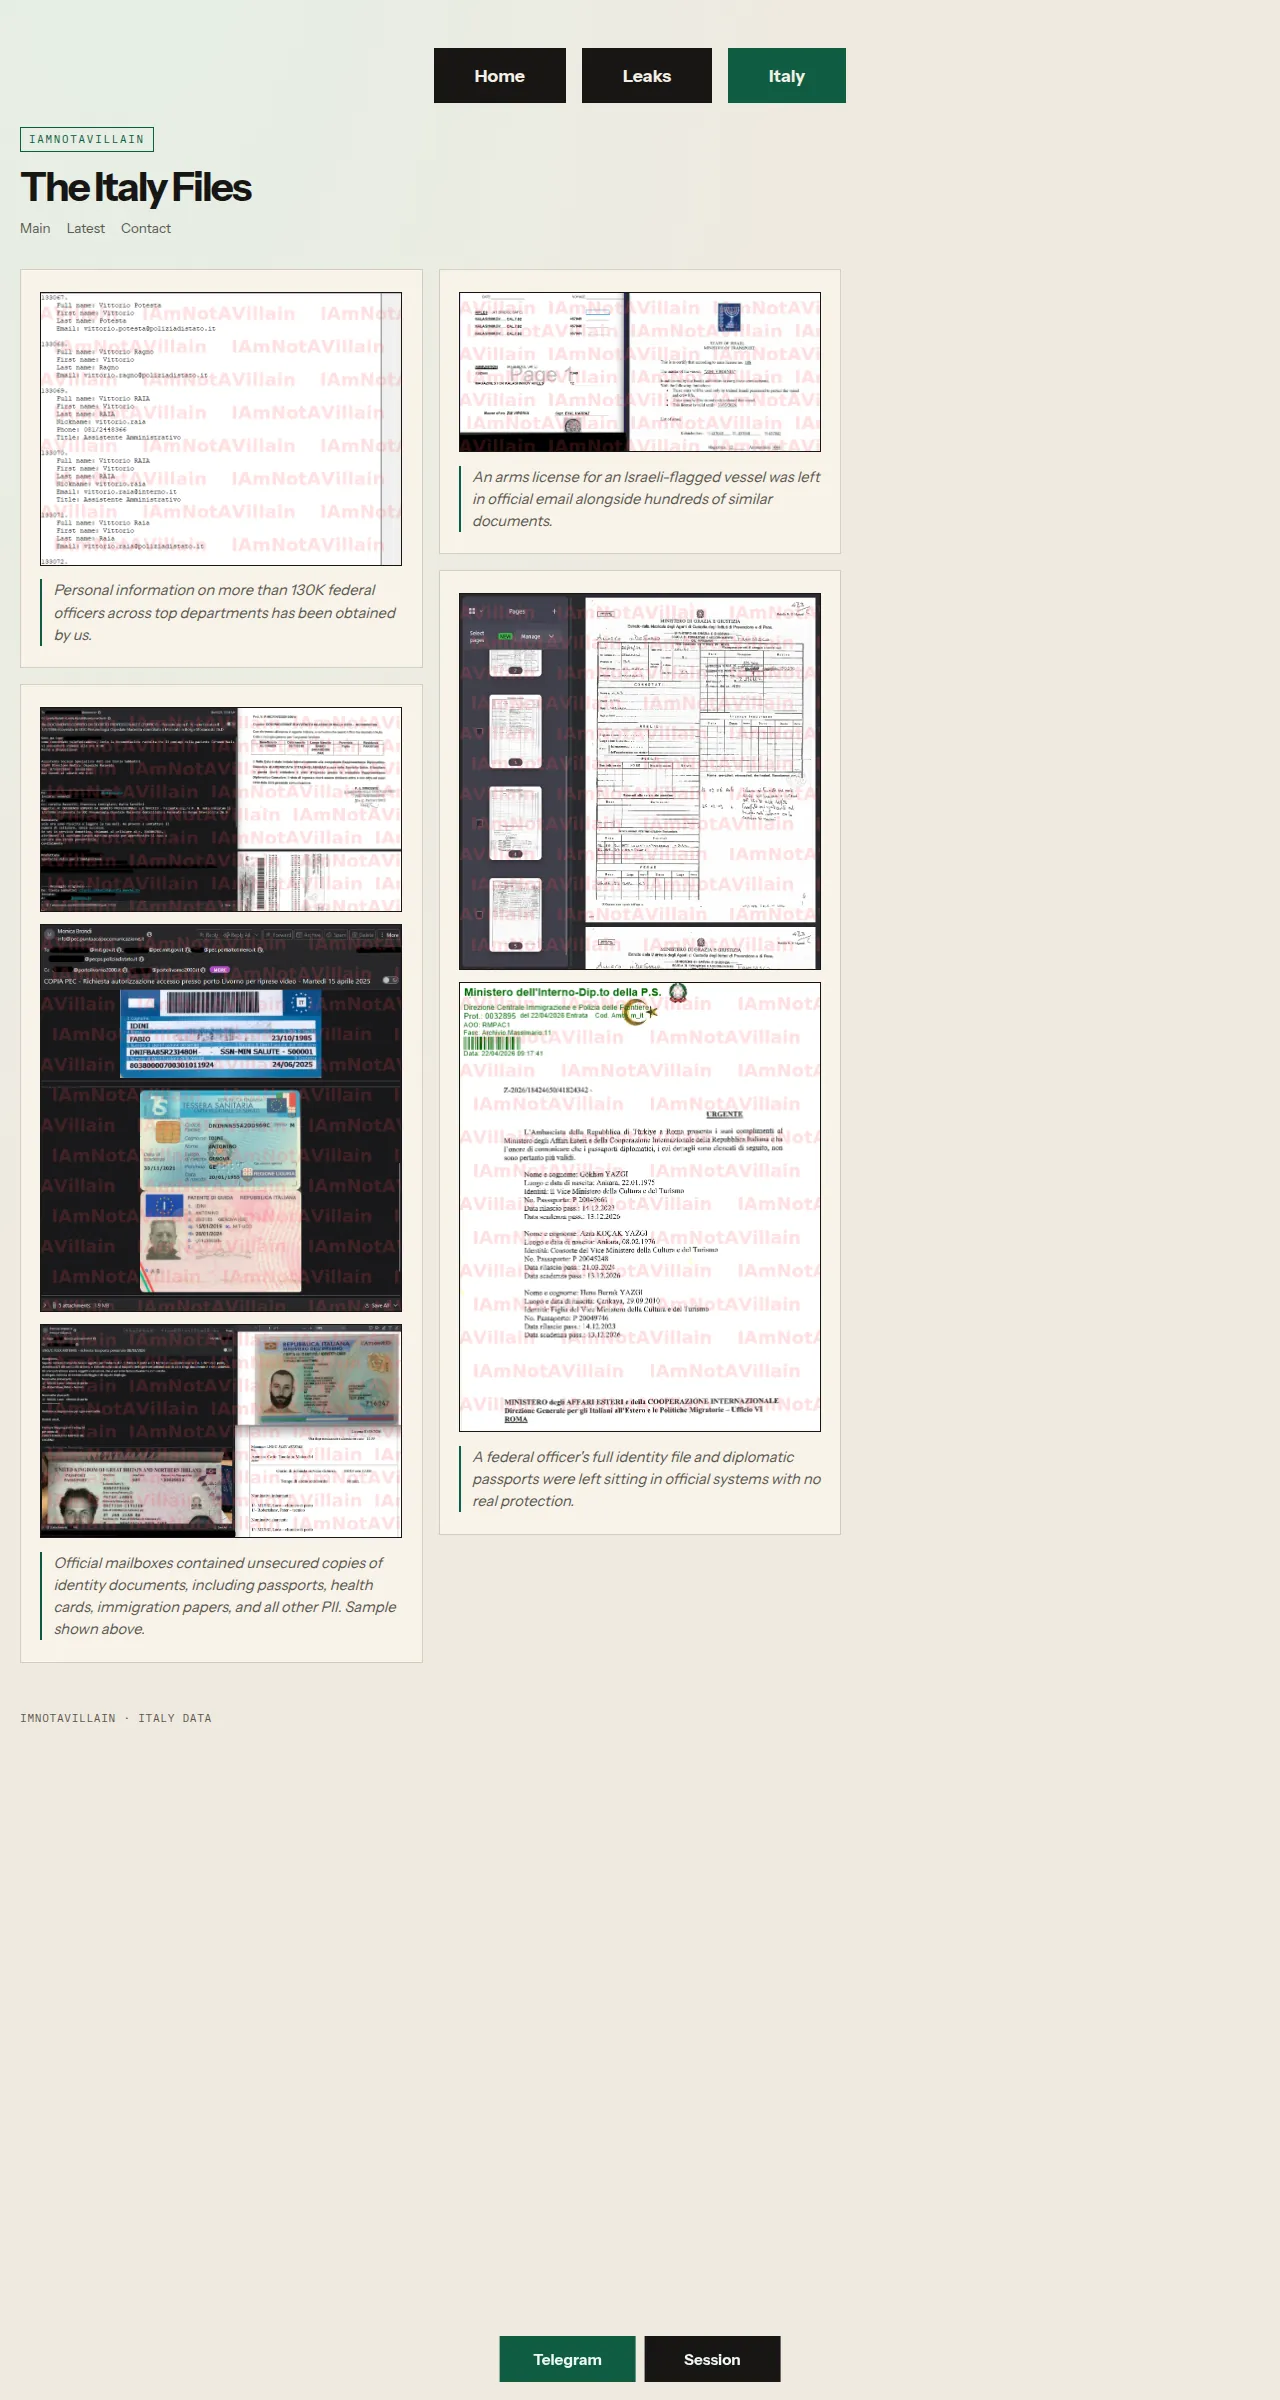
Proof files published by the operator — 7 image(s) harvested from this entry. Content is locked; type and dimensions shown.
Capture history — 5 day(s) tracked. Content is locked.