Rueegseggerag
medusalockerThis record tracks a ransomware attack claimed by the medusalocker group against Rueegseggerag. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
rueegseggerag.ch operates within the Swiss manufacturing and engineering sector, providing specialized industrial and technical services aligned with production and design workflows. As documented in the threat-intelligence index, this entity is categorized as a ransomware victim associated with the medusalocker threat actor. The classification reflects observed security event correlations without disclosing specific breach details, data exfiltration specifics, or unverified operational impacts. Understanding such listings aids defenders in contextualizing risk within industrial sectors and geographic regions. rueegseggerag.ch was listed as a ransomware victim associated with medusalocker.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-16. Verdict evidence: [H9] ⚠ Demo access — showing up to 10 files per folder. Full data will be available after publication.
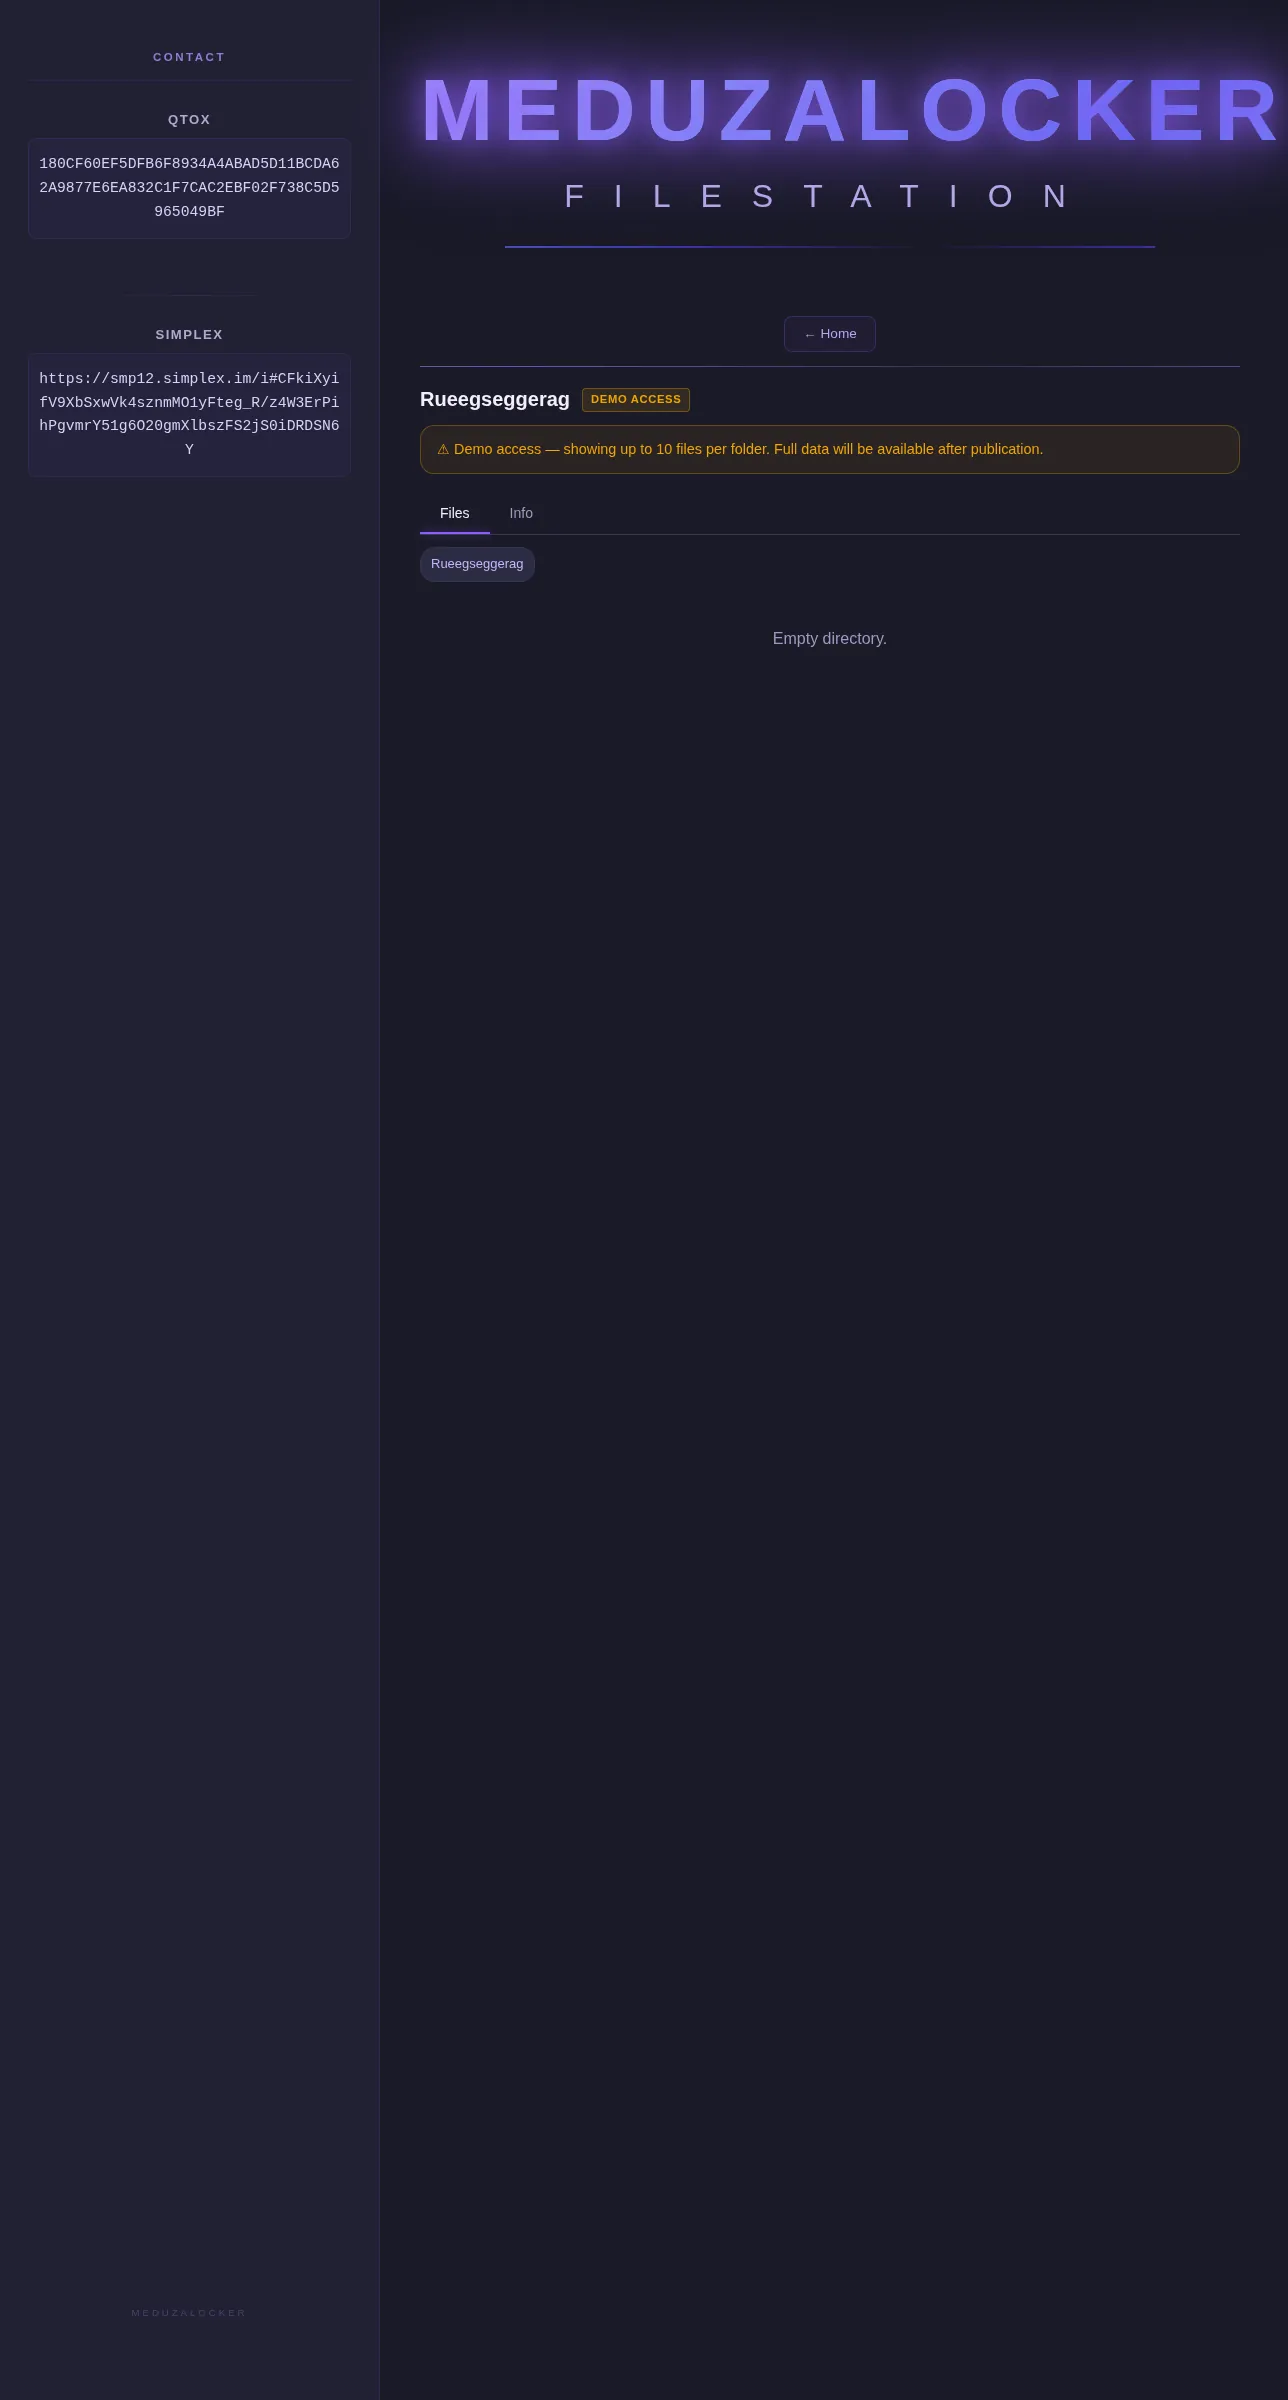
Capture history — 5 day(s) tracked. Content is locked.