This record tracks a ransomware attack claimed by the
rhysida group against
Noelker and Hull. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
7days open
t1 · Published
t2 · Pending
Indexed by Breach House
October 28, 2026
Leak Status
pending
checked 2026-11-02
Disclosed / Notified
Not disclosed yet
Attack Summary
noelkerhull.com is a domain identifier cataloged within a threat-intelligence index as a ransomware victim. The entity is associated with the threat actor rhysida, with country attribution set to the United States and sector information not specified in available data. This listing type indicates the entity's inclusion due to ransomware-related activity or impact, providing context for threat analysts tracking cyber incidents and associated actors. The description remains factual and neutral, avoiding speculation regarding specific breach details, data handling, or operational outcomes. It serves as a reference point for monitoring threat actor behavior and victim entity associations within cybersecurity intelligence frameworks.
Leak Screenshots
3 CAPTURED
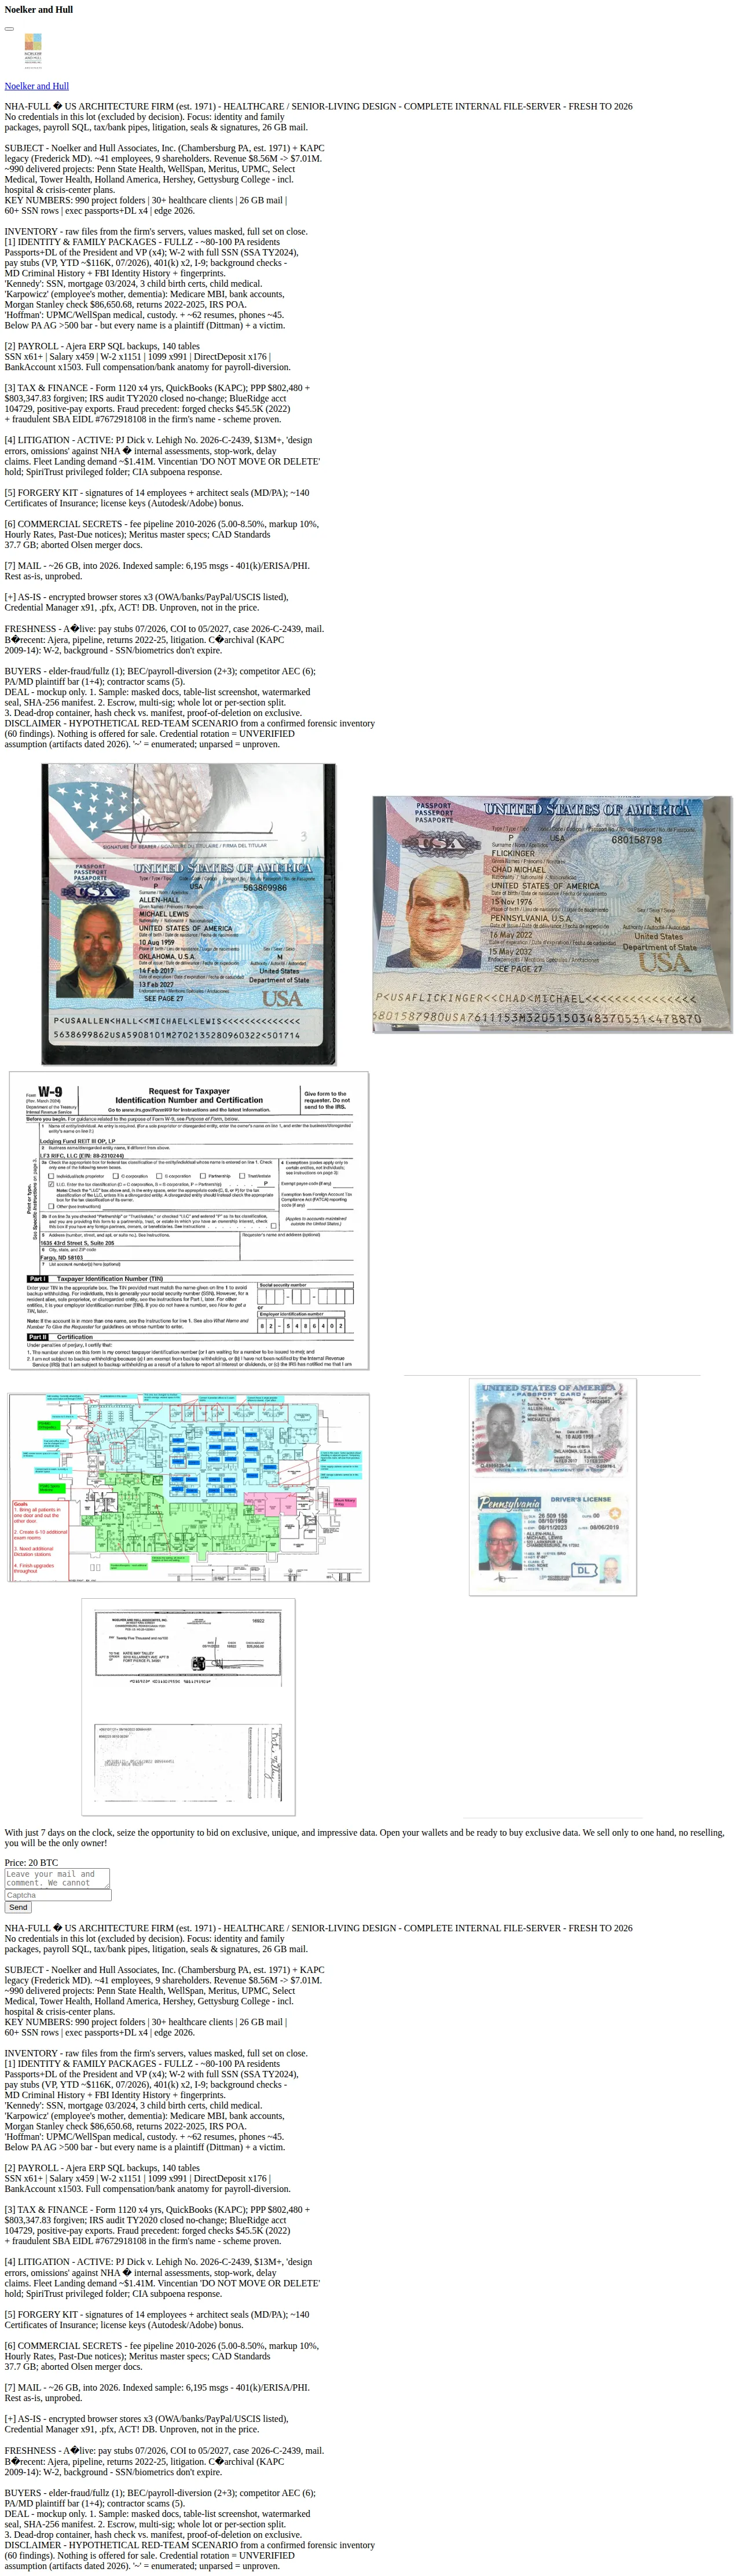
Captured directly from the operator's leak site by our collector, last checked 2026-11-02. Verdict evidence: [H10] Price: 20 BTC
Proof files published by the operator —
2 image(s) harvested from this entry.
Content is locked; type and dimensions shown.
Capture history —
2 day(s) tracked. Content is locked.
Showing the latest capture only
Unlock the 2 captures already taken, plus the 2 proof file(s) the operator published.
Dark Web Exposure
Findings for mail.subject
— indexed by HaveIBeenRansom.
2
found in Infostealer logs
0
found in Traditional breaches
0
found in Ransomware leaks
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
Full exposure is locked
See every breached email, the internal-vs-external split and each leak source behind this victim.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.