triniticaring.org
safepayThis record tracks a ransomware attack claimed by the safepay group against triniticaring.org. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
triniticaring.org operates within the NGO and associations sector and serves as a digital entity associated with the threat actor safepay in threat-intelligence records. Publicly available information does not confirm specific incident details such as data exfiltration scope, ransom demands, or operational impact; therefore, this entry describes the entity’s sector, geographic context, listing classification, and attacker association only. The organization’s inclusion reflects its identification within a ransomware victim index connected to safepay, a threat actor operating within the United States environment. This catalog description maintains neutrality and avoids speculative claims beyond verified indexing metadata.
Leak Screenshots
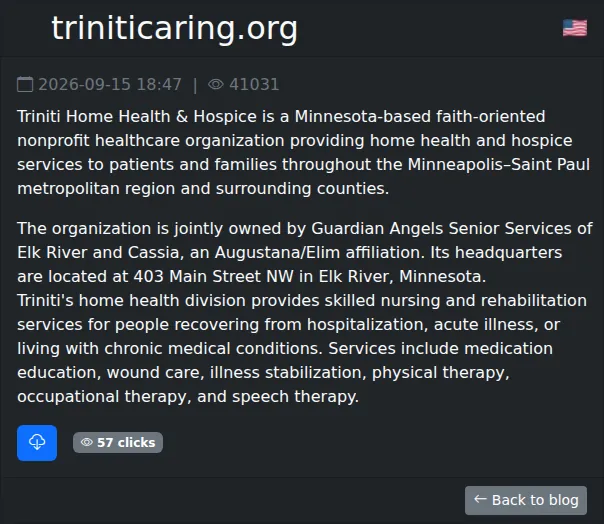
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-11-05. Verdict evidence: [S1] SafePay own post links the published dump server (http://a5d3otrzcgbprssbut7fm7ykl2edbcrhzxi3g3qhs327jwp44yovi2id.onion/triniticaring/)
Capture history — 3 day(s) tracked. Content is locked.