Europrim
thegentlemenThis record tracks a ransomware attack claimed by the thegentlemen group against Europrim. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
euro-prim.com operates within the Finance, Legal, and Insurance sectors and is headquartered in France. The entity provides specialized services aligned with financial compliance, legal advisory frameworks, and insurance operations. In the threat-intelligence index, euro-prim.com is cataloged as a ransomware victim linked to thegentlemen, indicating a cybersecurity incident involving this threat actor. The listing reflects the entity's association with this attack campaign without disclosing unverified details such as data stolen, ransom demands, or confirmed breach specifics. This entry serves to document the relationship between euro-prim.com and thegentlemen within the ransomware victim category for analytical and defensive reference.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-05. Verdict evidence: [M1] 200+ products; it holds a solid 4.2/5 rating on 222 Google reviews.
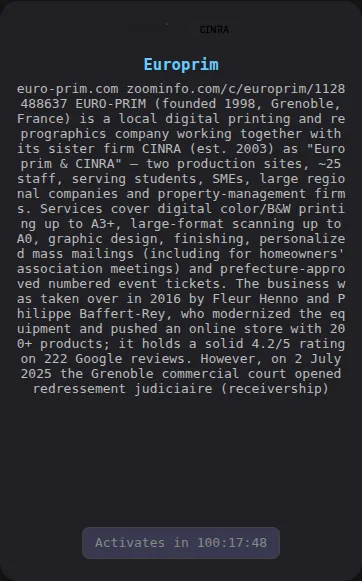
Capture history — 2 day(s) tracked. Content is locked.