Operation – “Enter Upon Them By The Gate” – 0x04 : Mann-shinnar
toufanThis record tracks a ransomware attack claimed by the toufan group against Operation – “Enter Upon Them By The Gate” – 0x04 : Mann-shinnar. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Operation Enter Upon Them By The Gate 0x04 : Mann-shinnar is cataloged as a ransomware victim entity within the IT sector, associated with the threat actor toufan. This operation represents an instance of ransomware activity targeting information technology environments, reflecting threat actor TTPs and victim impact patterns documented in the threat-intelligence index. The entity details contextualize the attack vector and sector exposure without disclosing unconfirmed specifics such as data exfiltration scope, ransom demands, or precise geographic origin. It was listed as a ransomware victim associated with toufan.
Leak Screenshots
16 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-19. Verdict evidence: [H9] We decided to release over 5GB of data containing thousands of documents including 800+ files of detailed designs for the aforementioned projects 🔻This is what was allowed to be published, and th
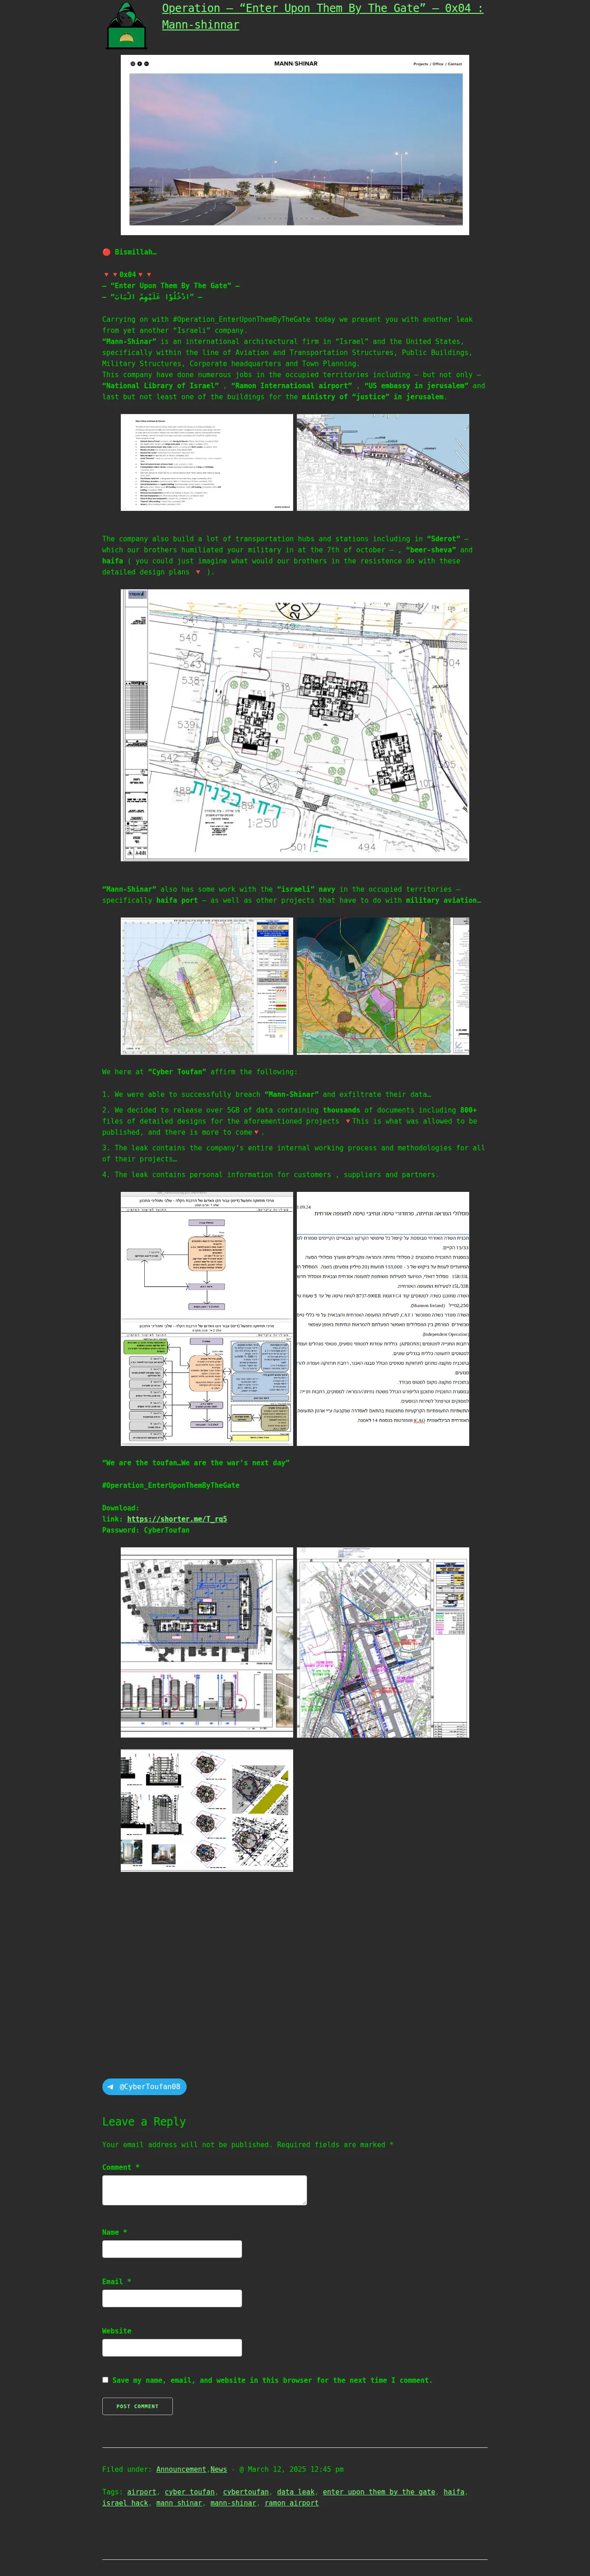
Proof files published by the operator — 15 image(s) harvested from this entry. Content is locked; type and dimensions shown.
Capture history — 4 day(s) tracked. Content is locked.