Gamdom V2
WhitearmorThis record tracks a ransomware attack claimed by the Whitearmor group against Gamdom V2. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Gamdom V2 is cataloged as a ransomware victim within the IT sector, with associated threat actor Whitearmor and country attribution listed as the United States. The entity represents an organization or system identified in threat-intelligence indexing under this ransomware victim classification. Details focus on the entity’s role in the threat landscape, its sector context, and its association with Whitearmor rather than speculative claims about stolen data, ransom terms, or confirmed breach specifics. This listing supports structured analysis of ransomware incidents and threat actor relationships across IT environments. Gamdom V2 was listed as a ransomware victim associated with Whitearmor.
Leak Screenshots
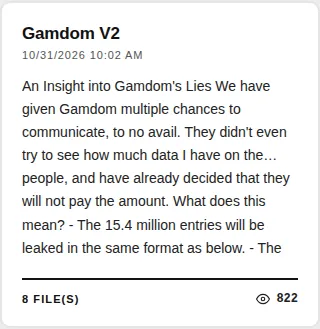
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-11-05. Verdict evidence: [H9] An Insight into Gamdom's Lies We have given Gamdom multiple chances to communicate, to no avail. They didn't even try to see how much data I have on the people, and have already decided that they
Capture history — 5 day(s) tracked. Content is locked.